01 / Security engineering
We build security your team can run.
AppSec, identity and detection, tied to the way you ship.
02 / AppSec
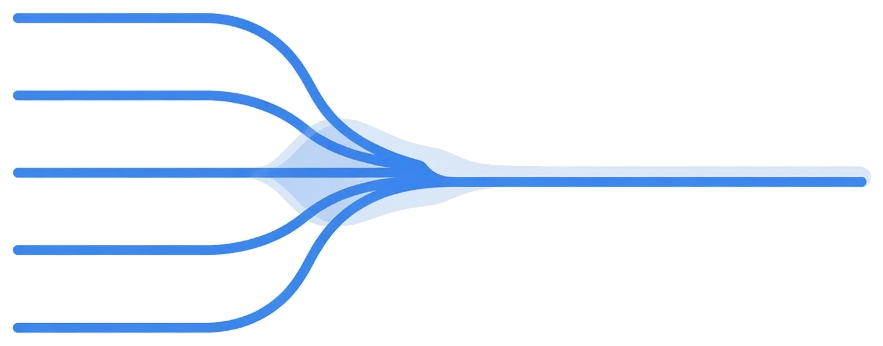
One process for scanners, owners and fixes.
SAST, DAST, SCA and container checks feed one flow. Each finding has an owner.
We implement Whitespots ASPM.
03 / Private scanners
Some checks must run inside your network.
Secret search in CI/CD, Nuclei templates and rules for your own code.
Merge request review: see TrustFlare AI Security Agent.
04 / Identity
We set up SSO, service identity and admin access.
We design access across the trust boundaries you really have.
Device trust: see TrustFlare Access.
05 / Detection
Detection and antifraud rules that stay useful after launch.
We connect signals to decisions, then tune the rules. Insider-threat work stays inside the privacy limits you set.
Antifraud: see SignalGate.
Questions
A few things to know
Do we have to buy Whitespots?
No. We work with the scanners you already have.
Who runs the result?
Your team. Handover is part of the work.
Can you work with Keycloak?
Yes. Keycloak and device trust are part of our work.
Will you watch our employees?
No. Detection stays inside the privacy limits you set.
Start with one problem
Bring the architecture and the people who will run it.
We design for the way you already ship.